
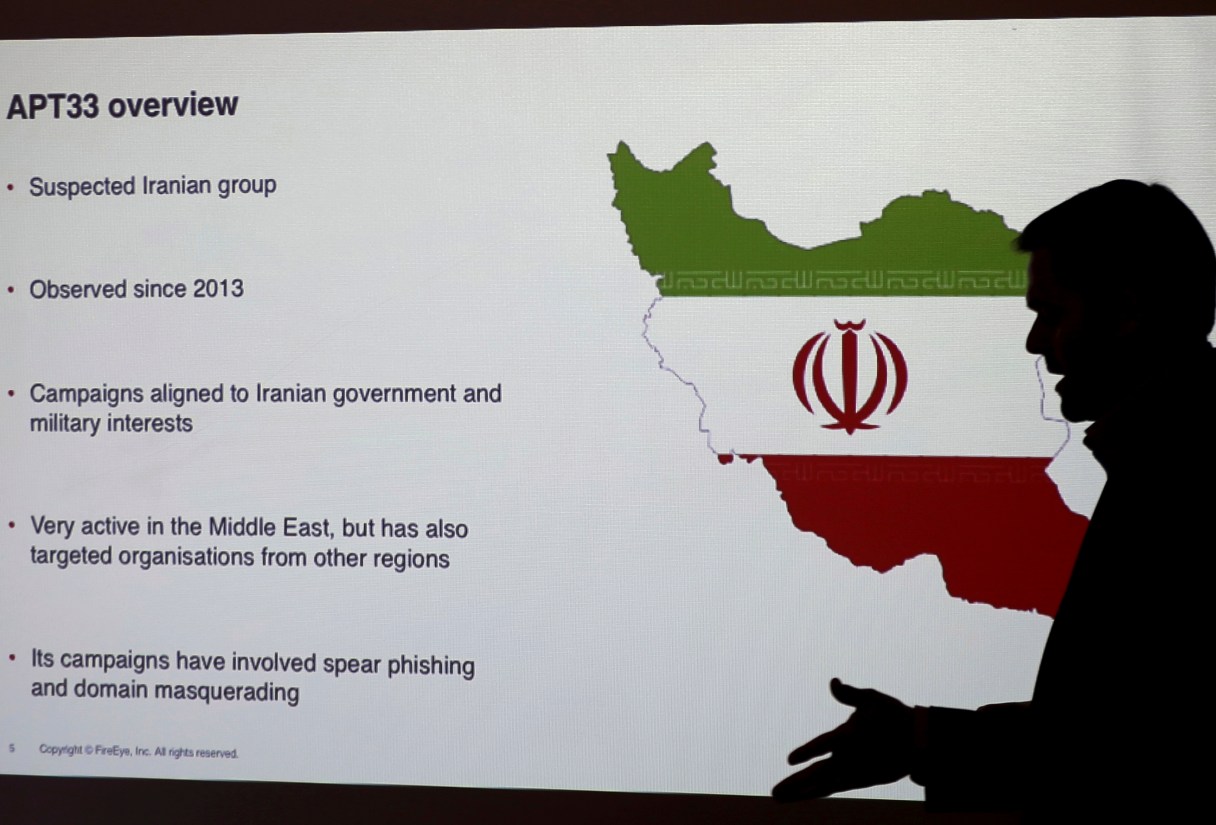
DUBAI, United Arab Emirates (AP) – A group of hackers suspected of working in Iran for its government is targeting the aviation and petrochemical industries in Saudi Arabia, the U.S. and South Korea, a cybersecurity firm warned Wednesday.
The report by FireEye also said the suspected Iranian hackers left behind a new type of malware that could have been used to destroy the computers it infected, an echo of two other Iran-attributed cyberattacks targeting Saudi Arabia in 2012 and 2016 that destroyed systems.
Iran’s office at the United Nations did not immediately respond to a request for comment Wednesday and its state media did not report on the claims. However, suspected Iranian hackers long have operated without caring if people found it was them or if there would be consequences, making them incredibly dangerous, said Stuart Davis, a director at one of FireEye’s subsidiaries.
“Today, without any repercussions, a neighboring country can compromise and wipe out 20 institutions,” Davis said.
FireEye refers to the group as APT33, an acronym for “advanced persistent threat.” They used phishing email attacks with fake job opportunities to gain access to the companies affected, faking domain names to make it look like the messages came from Boeing Co. or defense contractors.