
Friday, November 13, 2026Nov 13

Missed opportunities to stop OPM cyber breach spelled out

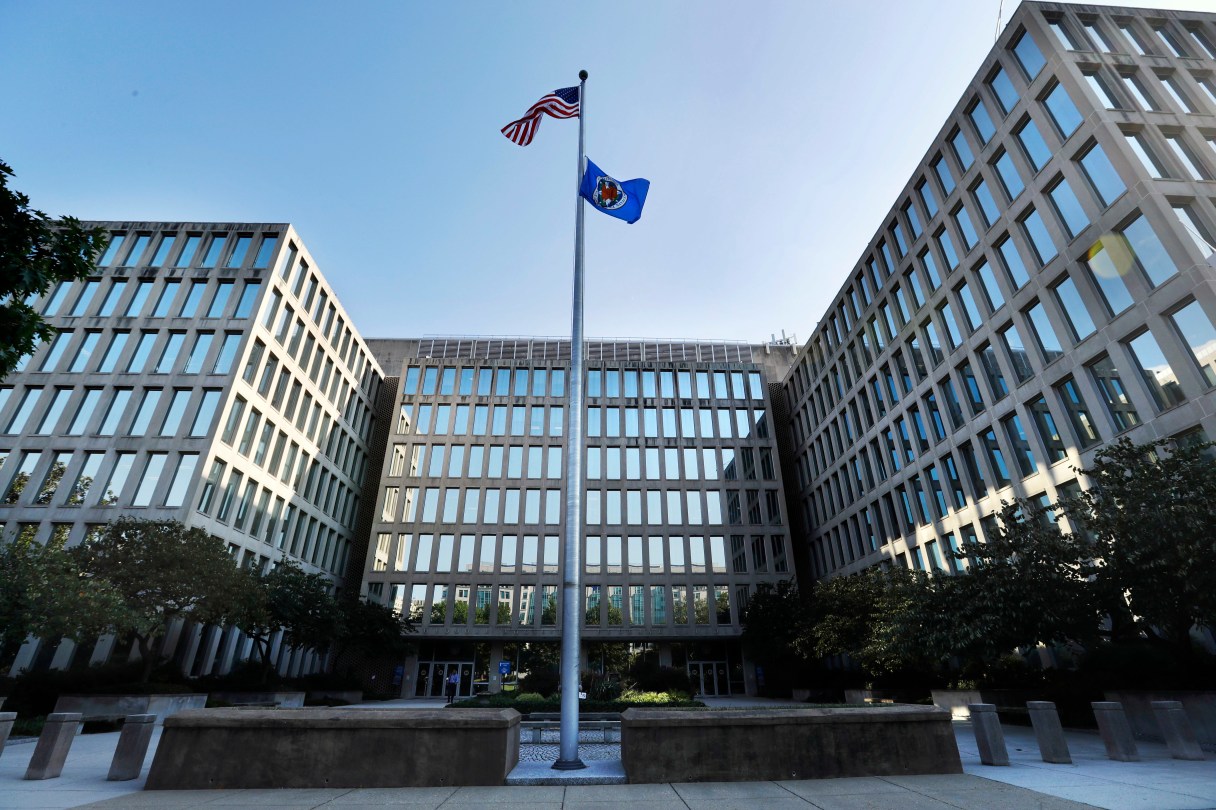
The U.S. Office of Personnel Management is photographed Tuesday, Sept. 6, 2016, in Washington. It was time to purge the hacker from the U.S. government’s computers. After secretly monitoring the hacker's online movements for months, officials worried he was getting too close to critical information and devised a plan to expel him. Trouble was, with all their attention focused in that case, they missed the other hacker entirely. A new congressional report provides previously undisclosed details and a behind-the-scenes chronology of one of the worst-ever cyberattacks on the United States, laying out missed opportunities before the break-in at the OPM exposed security clearances, background checks and fingerprint records. (AP Photo/Jacquelyn Martin)
The U.S. Office of Personnel Management is photographed Tuesday, Sept. 6, 2016, in Washington. It was time to purge the hacker from the U.S. government’s computers. After secretly monitoring the hacker's online movements for months, officials worried he was getting too close to critical information and devised a plan to expel him. Trouble was, with all their attention focused in that case, they missed the other hacker entirely. A new congressional report provides previously undisclosed details and a behind-the-scenes chronology of one of the worst-ever cyberattacks on the United States, laying out missed opportunities before the break-in at the OPM exposed security clearances, background checks and fingerprint records. (AP Photo/Jacquelyn Martin) The U.S. Office of Personnel Management is photographed Tuesday, Sept. 6, 2016, in Washington. It was time to purge the hacker from the U.S. government’s computers. After secretly monitoring the hacker's online movements for months, officials worried he was getting too close to critical information and devised a plan to expel him. Trouble was, with all their attention focused in that case, they missed the other hacker entirely. A new congressional report provides previously undisclosed details and a behind-the-scenes chronology of one of the worst-ever cyberattacks on the United States, laying out missed opportunities before the break-in at the OPM exposed security clearances, background checks and fingerprint records. (AP Photo/Jacquelyn Martin)

WASHINGTON (AP) – It was time to purge the hacker from the U.S. government’s computers. After secretly monitoring the hacker’s online movements for months, officials worried he was getting too close to critical information and devised a plan, dubbed “the Big Bang,” to expel him.

Trouble was, with all their attention focused in that case, they missed the other hacker entirely.

A new congressional report provides previously undisclosed details and a behind-the-scenes chronology of one of the worst-ever cyberattacks on the United States, laying out missed opportunities before the break-in at the Office of Personnel Management exposed security clearances, background checks and fingerprint records. That attack – widely blamed on China’s government – compromised personal information of more than 21 million current, former and prospective federal employees, led to the resignation of the OPM director and drew outrage over changing explanations about the hack’s seriousness.

The report by the House Committee on Oversight and Government Reform faulted the personnel agency for failing to secure sensitive data despite warnings for years that it was vulnerable to hackers. It concluded that the hacking revealed last year could have been prevented if OPM had put in place basic, required security controls and recognized from an earlier break-in that it was actually dealing with a sophisticated, persistent enemy.

“We have literally tens of millions of Americans whose data was stolen by a nefarious overseas actor, but it was entirely preventable,” Rep. Jason Chaffetz, a Utah Republican and committee chairman, said in an interview.